### Author:  [@patrick](https://community.zammad.org/u/patrick)
#### Post date: [October 9, 2020, 10:10pm UTC](https://community.zammad.org/t/security-questions/5455/1 "2020-10-09T22:10:26Z")
### Infos:
- Used Zammad version: 3.5.x
- Used Zammad installation source: (source, package, …) Ubuntu via DEB
- Operating system: Ubuntu 18.04
- Browser + version:
Hello,
I’m a complete newbie with Zammad and I’m not very good with servers and Linux operating systems. Please excuse me if my questions are too “beginnerish”.
- I have installed Zammad exactly according to the instructions.
[https://docs.zammad.org/en/latest/install/ubuntu.html](https://docs.zammad.org/en/latest/install/ubuntu.html)
- I also installed Elasticsearch according to the instructions
[https://docs.zammad.org/en/latest/install/elasticsearch.html](https://docs.zammad.org/en/latest/install/elasticsearch.html)
(before Zammad)
Here my first question : Is the step “Optional settings” -\> HTTP Basic auth necessary ? If so, when and why ?
Then I enabled SSL according to this file (and the instructions in it) and used this .conf file.
>
Zammad should be accessible from outside via a URL.
Now the second question is: Have I done all the security things I need to make sure that Zammad is reachable from the outside with the above mentioned installation ?
And my last question :
Which updates should I run regularly (how often) to keep the system secure?
Thanks for your help and support !
---
### Author:  [@klausneil](https://community.zammad.org/u/klausneil)
#### Post date: [October 15, 2020, 10:23pm UTC](https://community.zammad.org/t/security-questions/5455/2 "2020-10-15T22:23:19Z")
Hi @patrick well the first question is about the conection http by default. well for security reason is very import use https for traffic encrypt, also they say how can create a certificate free with letsencrypt this is very good and important.
The type of access is by your desicion if only your agents have access to the system in lan network then the services not be public but if your system is accesible for agent and customers them the services have public in internet, yet this with protection of firewall and others devices.
---
### Author:  [@patrick](https://community.zammad.org/u/patrick)
#### Post date: [October 16, 2020, 7:25am UTC](https://community.zammad.org/t/security-questions/5455/3 "2020-10-16T07:25:29Z")
Hello, Klaus,
thanks for your feedback.
In my case Zammad, Elastic and Postgres are running on the same Linux server. The traffic between zammad \<-\> Elastic \<-\> Postgres is only “internal”. Is it also necessary to switch to SSL ?
From outside only port 443 is open for https. All other incoming ports are not accessible.
---
### Author:  [@patrick](https://community.zammad.org/u/patrick)
#### Post date: [October 16, 2020, 8:44am UTC](https://community.zammad.org/t/security-questions/5455/4 "2020-10-16T08:44:16Z")
Unfortunately I do not know my way around that well.
If I install Zammad via DEB, will all security related topics be activated ?
I assume that SSL is already active.
(When I open postgresql.conf, ssl = on, also certificates are already created. In pg\_hba.conf i think only internal traffic is allowed
host all all ::1/128
local replication all
host replication all 127.0.0.1/32
host replication all ::1/128 )
These settings should be safe, right?
---
### Author:  [@klausneil](https://community.zammad.org/u/klausneil)
#### Post date: [October 16, 2020, 3:37pm UTC](https://community.zammad.org/t/security-questions/5455/5 "2020-10-16T15:37:03Z")
Hi @patrick dont worry for this exist forums as this, well all services have configurations by defaults and this is very vulnerable; if you need security for a services as zammad postfix iis and others services, you need have know about admin network, this is very import cause many services need hardening in security on the configuration, you can configure the base but if you need security in deep you will need a specialist and devices of security as firewall, webcontrol and endpoint protection.
For the example as you say the ssl is on but this certificates have a encryptation standar, secure for internal service but very insecure if this service is public on internet.
**When I open postgresql.conf, ssl = on, also certificates are already created. In pg\_hba.conf i think only internal traffic is allowed**
I hope clarifyed your questions and if you have more can tell me.
**Update:**
> _Hola, Klaus,_
>
> _gracias por sus comentarios._
>
> _En mi caso, Zammad, Elastic y Postgres se ejecutan en el mismo servidor Linux. El tráfico entre zammad ↔ Elastic ↔ Postgres es solo “interno”. ¿También es necesario cambiar a SSL?_
> _Desde el exterior, solo el puerto 443 está abierto para https. Todos los demás puertos entrantes no son accesibles._
I didn’t see this, yes is ok that postgresql have ssl internal and also is ok that only you have a https (443/tcp) enable in your firewall, here all is ok but dont forget that your certificate ssl must have a signature of some entity (comodo, verising, sysmantec, lettsencypt, etc) for security reasons and remenber the security is also internal as external.
---
### Author:  [@patrick](https://community.zammad.org/u/patrick)
#### Post date: [October 16, 2020, 4:59pm UTC](https://community.zammad.org/t/security-questions/5455/6 "2020-10-16T16:59:46Z")
Hi Klaus,
thank you very much.
For nginx i have already a letscencrypt certificate.
Can I use this directly ?
---
### Author:  [@klausneil](https://community.zammad.org/u/klausneil)
#### Post date: [October 16, 2020, 9:27pm UTC](https://community.zammad.org/t/security-questions/5455/7 "2020-10-16T21:27:53Z")
Hi @patrick,exactly is a very good certificate i aslo use this entity.
---
### Author:  [@patrick](https://community.zammad.org/u/patrick)
#### Post date: [October 16, 2020, 11:07pm UTC](https://community.zammad.org/t/security-questions/5455/8 "2020-10-16T23:07:32Z")
ssl\_cert\_file
ssl\_key\_file
I have this key´s stored in the directory
cert,chain,fullchain and privkey.pem
is the ssl\_cert\_file = cert.pem and the ssl\_key\_file = privkey.pem ?
Should I only change the two Key’s ? Or do I have to pay attention to something else ?
---
### Author:  [@klausneil](https://community.zammad.org/u/klausneil)
#### Post date: [October 26, 2020, 11:25pm UTC](https://community.zammad.org/t/security-questions/5455/9 "2020-10-26T23:25:44Z")
Hi @patrick sorry by the delay, well if you can see you need put the path of the Lets Encrypt
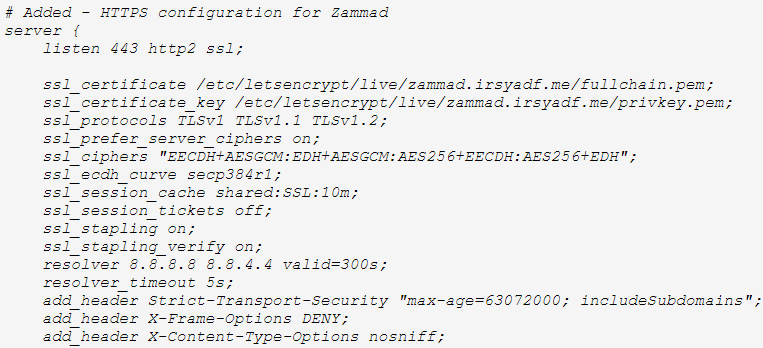
Well i recommend follow this link.
> **[How to Setup Zammad Ticketing System on Ubuntu 16.04](https://www.howtoforge.com/tutorial/how-to-setup-zammad-ticketing-system-on-ubuntu-1604/)**
>
> Zammad is an open source helpdesk/customer support system written in Ruby. Its a web-based ticketing system with many features, including support to ...
---
### Author:  [@rsysadmin](https://community.zammad.org/u/rsysadmin)
#### Post date: [November 1, 2020, 9:32am UTC](https://community.zammad.org/t/security-questions/5455/10 "2020-11-01T09:32:36Z")
Hi all,
please refer to my post
> [@Making Zammad a bit more secure](https://community.zammad.org/t/making-zammad-a-bit-more-secure/5584):
>
> Hi all, this link is quite useful if you want to make your web server a bit more secure. Please try to implement TLS 1.3 if you can. Best, Martin
and try to implement TLS 1.3 if you can.
TLS 1.1 is discouraged and soon will be TLS 1.2 …
Best,
Martin
---
### Author:  [@klausneil](https://community.zammad.org/u/klausneil)
#### Post date: [November 3, 2020, 12:24am UTC](https://community.zammad.org/t/security-questions/5455/11 "2020-11-03T00:24:33Z")
Of course, security is more about hardening tomcat, apache, nginx; Apart from the encryption as you comment, it is also to hide information from the service such as banner grabbing among other techniques.
---
### Author:  [@system](https://community.zammad.org/u/system)
#### Post date: [March 3, 2021, 12:24am UTC](https://community.zammad.org/t/security-questions/5455/12 "2021-03-03T00:24:39Z")
This topic was automatically closed 120 days after the last reply. New replies are no longer allowed.