# LDAP: Integrate group as user
**URL:** https://community.zammad.org/t/ldap-integrate-group-as-user/19594
**Category:** Technical assistance
**Created:** [February 13, 2026, 7:54am UTC](https://community.zammad.org/t/ldap-integrate-group-as-user/19594 "2026-02-13T07:54:03Z")
**Posts on this page:** 3
**Page:** 1
### Author:  [@Heike](https://community.zammad.org/u/Heike)
#### Post date: [February 13, 2026, 7:54am UTC](https://community.zammad.org/t/ldap-integrate-group-as-user/19594/1 "2026-02-13T07:54:03Z")
### Infos:
- Used Zammad version: 6.5.1-1757083311.14056d81.bookworm
- Operating system: Linux
- Browser + version: Firefox 147.0.3
### Expected behavior:
- Integrate the group as a user and according to the selection. Group members should not be integrated as users.
### Actual behavior:
- The LDAP integration failed
### Steps to reproduce the behavior:
- Extension of group attributes to include uid and objectguid, but the error persists.
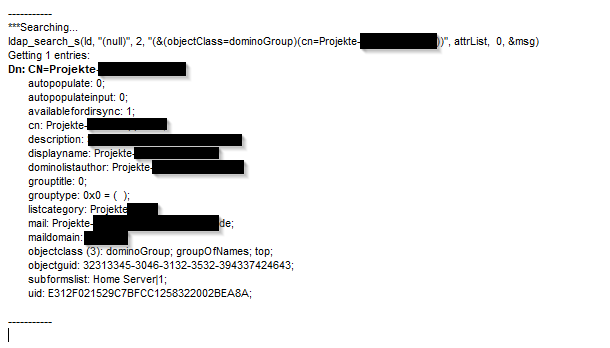
The LDAP query via an LDP console returns the following result:
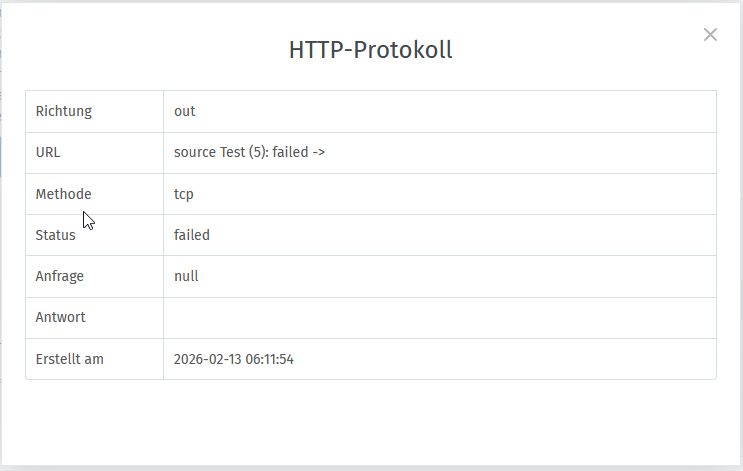
The same LDAP query string in Zammad returns the following result:
The following settings were made under Integration - LDAP:
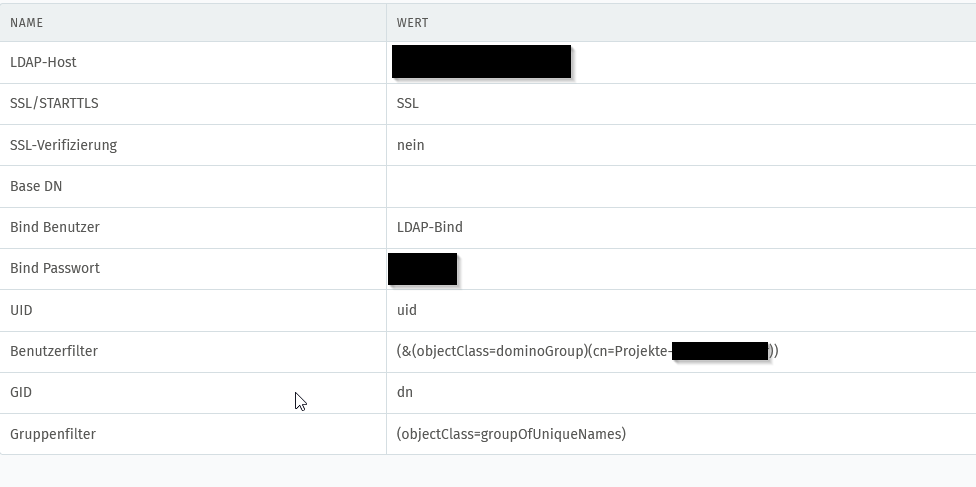
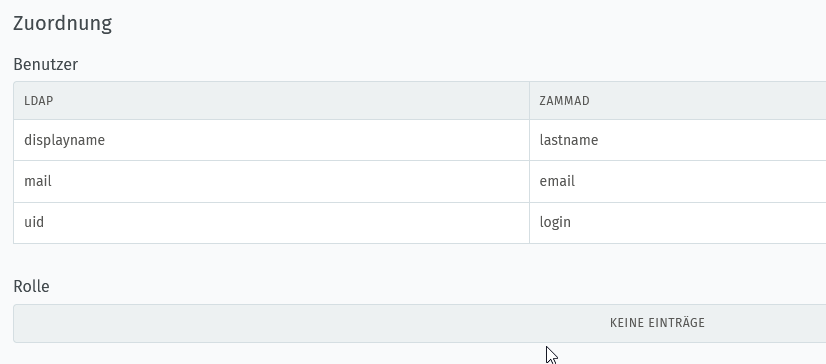
People can be successfully integrated via the LDAP integration. The same LDAP host and the same access data are used.
Is it not possible to integrate groups in this way? How else can I integrate groups as users?
The reason for this is that in certain cases, which are to be controlled by triggers, an email is sent to the group’s email address.
---
### Author:  [@Heike](https://community.zammad.org/u/Heike)
#### Post date: [March 20, 2026, 3:41pm UTC](https://community.zammad.org/t/ldap-integrate-group-as-user/19594/2 "2026-03-20T15:41:38Z")
We found a solution to our problem.
We linked the LDAP groups to Zammad roles, which in turn were assigned to their own Zammad groups.
---
### Author:  [@system](https://community.zammad.org/u/system)
#### Post date: [March 27, 2026, 3:42pm UTC](https://community.zammad.org/t/ldap-integrate-group-as-user/19594/3 "2026-03-27T15:42:26Z")
This topic was automatically closed 7 days after the last reply. New replies are no longer allowed.